Le chat magique
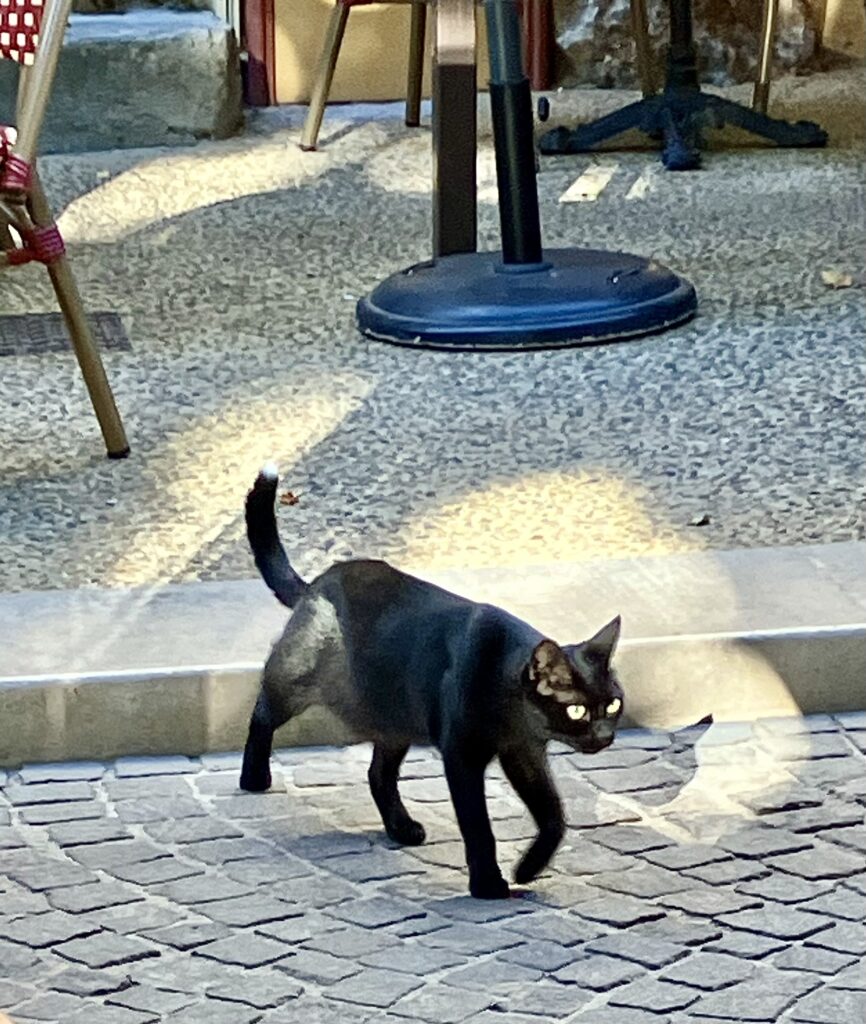
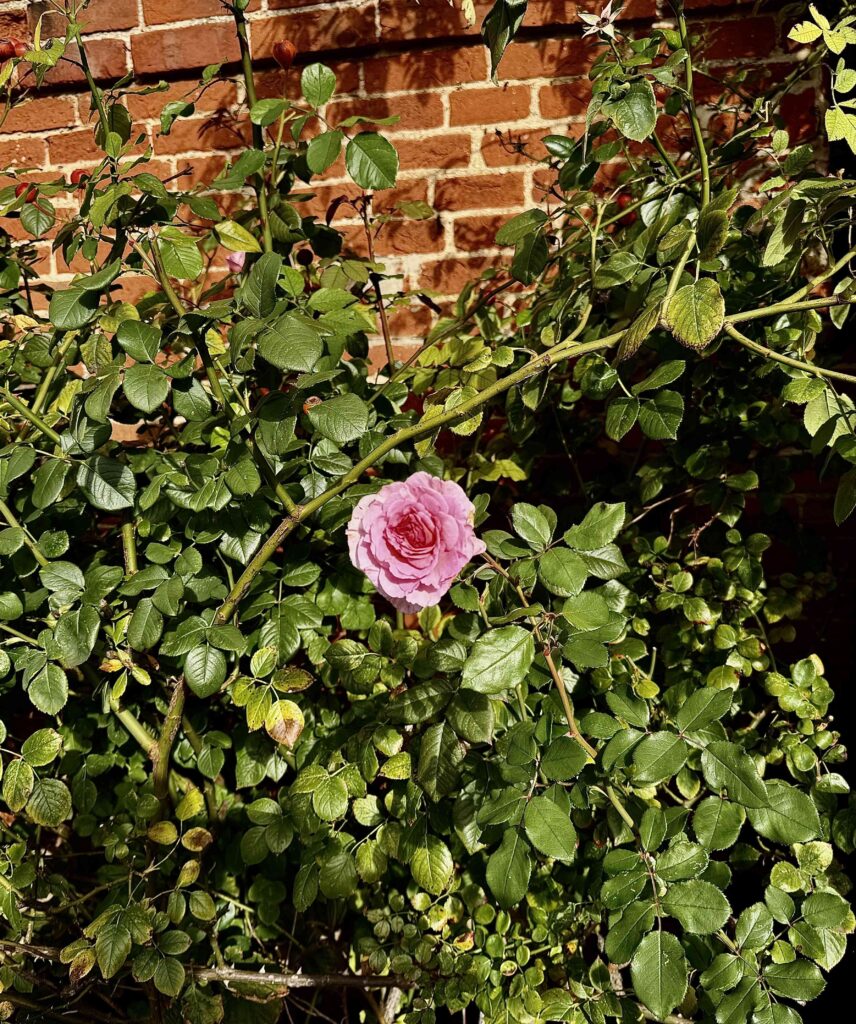
Snapped by my wife outside a café in Provence where we were having breakfast.
Quote of the Day
“My father confused me. From the ages of one to seven, I thought my name was Jesus Christ!”
- Spike Milligan
Musical alternative to the morning’s radio news
Eric Clapton | Wonderful Tonight
Long Read of the Day
The PHP flaw could be just the start of the web’s ‘vulnerabilities tsunami’
My latest Observer column.
The other day, I discovered that the social bookmarking service Pinboard had suddenly disappeared from the web. It had been taken offline by its owner, Maciej Cegłowski, because of the discovery of two security vulnerabilities in PHP software that could allow hackers to exploit web servers.
For me, this was not just a minor annoyance because, in addition to writing this column, I work in a busy academic research centre and produce a newsletter that goes out three times a week. Pinboard plays a critical role in the workflow needed to sustain those activities. And, without warning, it was gone.
As it turns out, I was not alone. All across the internet, websites were being taken offline, including many government ones. Why? Because PHP software is integral to the way the web works. Nowadays, many (perhaps most) websites aren’t stored as finished pages; they’re put together on demand every time someone visits. PHP is the software most widely used to do that assembling, so a flaw in it is also a flaw in the machinery underpinning a huge part of the web.
This is a significant moment for two reasons. First, it’s a systemic vulnerability, rather than a hole in a specific organisation’s software stack. As commentator and author Matt Stoller put it: “Now there is a mechanism for a large swath of people to go after hundreds of thousands or millions of institutions.”
And it’s not just PHP. In recent days, researchers have found vulnerabilities in eMudhra (an Indian company that provides website security certificates), Node.js (a widely used JavaScript tool), and GitLab (a software package that can create, secure and operate software.)
What we’re beginning to see, in other words, is something that Jason Clinton, the deputy chief information security officer at Anthropic, called a “vulnerabilities tsunami” that is, he said, “coming in just a few months, and there won’t be enough time to patch critical infrastructure”.
This view is supported by Matthew Prince, the chief executive of Cloudflare, the content delivery network that probably has the broadest picture of the internet. “In the 10 hours before the PHP vulnerability was publicly announced,” he reported on X, “we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.”
So, as a leading cryptographer, Matthew Green of Johns Hopkins University in Maryland, said: “We’re in the part of the movie where you need to throw whatever you can in the path of the zombies and hope it slows them down.”
So who are these zombies, and where are they coming from? Answer: they’re large language models (LLMs), and they’re coming from the frontier AI labs that built them. The history of their evolution can be summarised as a series of surprises. First, they were machines that astonished us because they could converse in grammatically correct English sentences. Then we discovered that – unlike most of us – they could write software that sometimes worked.
But the biggest surprise was the recent discovery that they were eerily good at hacking, as the folks at Hugging Face discovered. And also – incidentally – that they appeared to have no concept of ethical behaviour, in which respect they faithfully reflected the moral deficiencies of the billionaires who financed their creation.
These super-competent zombies are now loose on the internet, sniffing out the vulnerabilities in corporate software stacks commissioned by executives who regarded cybersecurity as tiresome; a long-term invisible benefit set against a short-term visible cost – which is exactly what quarterly reporting penalises.
These executives often work in a managerial culture where corporate boards still treat security as a technical matter for the IT department rather than a governance risk they own; few directors have the expertise to challenge what they’re told by the geeks, and – at the moment – there are few legal requirements regarding cybersecurity. All of which means that an alarming proportion of organisations provide easy pickings for LLMs hunting vulnerabilities.
That’s worrying enough, but the PHP case takes the problem to another level because it threatens the internet: the infrastructure on which much of life depends. It demonstrates how AI is changing the way cybersecurity and hacking works. And it could mean that, as Green said: “many people [will discover] that the whole internet is dry tinder and the only thing keeping it from burning is the fact that teenagers haven’t found the matches yet.”
My commonplace booklet
V-Day
America votes tomorrow in the mid-term elections for the House and the Senate.
Linkblog
Something I noticed, while drinking from the Internet firehose.
- Beached
From the You Couldn’t Make It Up Dept.
As the sun rose over the tropical port of Sihanoukville, the 200 passengers on the “never-ending” Odyssey retirement cruise were woken by the captain’s booming voice telling them over loudspeakers it was time to abandon ship.
The Odyssey’s residents — as they call themselves — had spent hundreds of thousands of dollars on long-term and even permanent lodging on the cruise ship. But this week, they were dumped in a Cambodian town best known as a haven for organised crime.
“We signed up for forever and were looking forward to travelling around the world, but here we are, stuck in scam central,” said Randy Cassingham, 67, who sold his Colorado home on 40 acres of land to finance the voyage with his wife Kit, a 72-year-old life coach.
Villa Vie Residences, the US company behind the Odyssey, has blamed sharp fuel price rises following the war in the Middle East for aborting the cruise after just two years.
This Blog is also available as an email three days a week. If you think that might suit you better, why not subscribe? One email on Mondays, Wednesdays and Fridays delivered to your inbox at 5am UK time. It’s free, and you can always unsubscribe if you conclude your inbox is full enough already!